A CISO has to decide whether the incident desk can tell, within six hours, which events must go to CERT-In, and whether the company can hand over 180 days of logs when asked. CERT-In's directions of 28 April 2022, made under section 70B(6) of the IT Act, require reporting within six hours of noticing an incident and logs kept securely in India for a rolling 180 days, as summarised by Linklaters. They took effect on 27 June 2022.
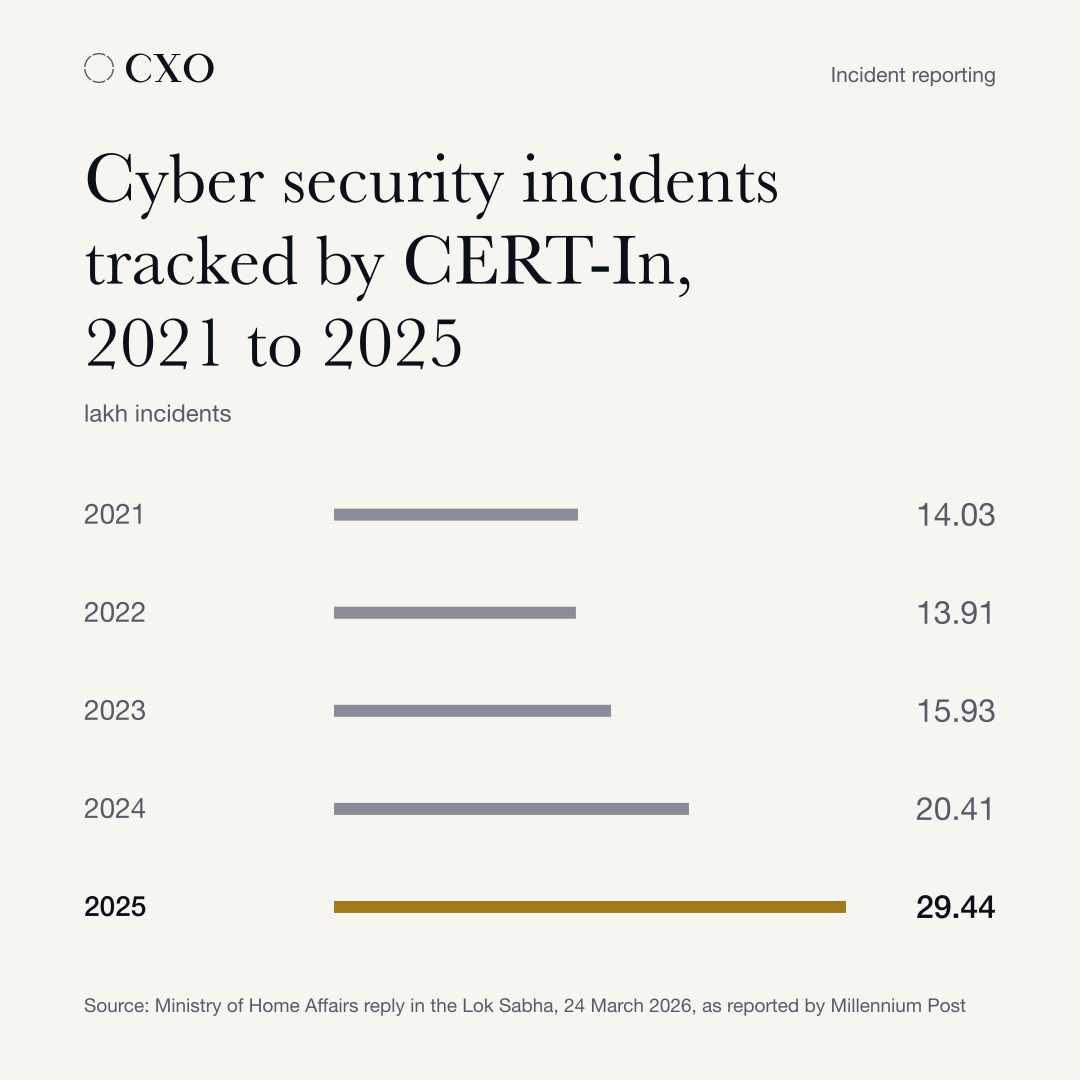
The volume behind that clock has doubled. Answering in the Lok Sabha on 24 March 2026, Minister of State for Home Bandi Sanjay Kumar gave CERT-In's counts: 14.03 lakh incidents in 2021, 13.91 lakh in 2022, 15.93 lakh in 2023, 20.41 lakh in 2024 and 29.44 lakh in 2025, as reported by Millennium Post. The same reply said CERT-In does not keep details of financial losses from incidents.
The core rules have stayed as written in 2022. The one relief came in June 2022, when CERT-In moved the deadline to 25 September 2022 for MSMEs and for the customer validation duties of data centre, cloud and VPN providers, as reported by Outlook Business, after ExpressVPN removed its servers from India. The penalty has changed. The Jan Vishwas Bill, as passed by the Lok Sabha in 2023, replaces "one lakh" with "one crore" in section 70B(7) and leaves the one-year prison term in place; K&S Partners reports the IT Act changes in force from November 2023. We found no public record of a prosecution under section 70B(7) since 2022.
The second change arrives through audit. AZB & Partners reports that CERT-In's audit guidelines of 25 July 2025 require empanelled auditors to verify compliance with the 2022 directions in every audit and report the findings with evidence, and to share audit reports with CERT-In within 5 days of completion. A missed report or a gap in log retention is therefore likely to reach CERT-In in writing, through your own auditor.
Our judgment is that enforcement for most companies will come through audit findings and sector regulators well before any prosecution, so dated evidence of each report sent within six hours, and logs that can actually be retrieved across the full 180 days, will count for more than the policy document. We are wrong if the government or CERT-In publicly reports a prosecution or fine under section 70B(7) against a private company before the end of 2027.
We would test this quarter: take the incidents logged in the past year, measure the time from detection to the CERT-In report, and pull logs from the oldest end of the 180-day window for the systems involved. Check that clocks still synchronise with the NIC or NPL time servers the directions name, as Linklaters notes, because a report built on unsynchronised logs is hard to defend.
This is based on our research into public sources and is not legal advice. Check how it applies to your company with your lawyers and advisers.
Sources (6)
- Linklaters, India: a new and onerous cyber security framework, with breach reporting obligations (25 May 2022)
- Millennium Post, Delhi tops cybersecurity incidents as cases double nationwide since 2021: Govt (24 March 2026)
- Outlook Business, New cybersecurity norms: CERT-In extends three months for VPNs to comply with rules (28 June 2022)
- PRS Legislative Research, The Jan Vishwas (Amendment of Provisions) Bill, 2023 as passed by Lok Sabha
- K&S Partners, Jan Vishwas Act amends provisions of the IT Act (28 February 2024)
- AZB & Partners, Strengthening India's cyber defence: CERT-In's new cyber security audit guidelines decoded (1 August 2025)